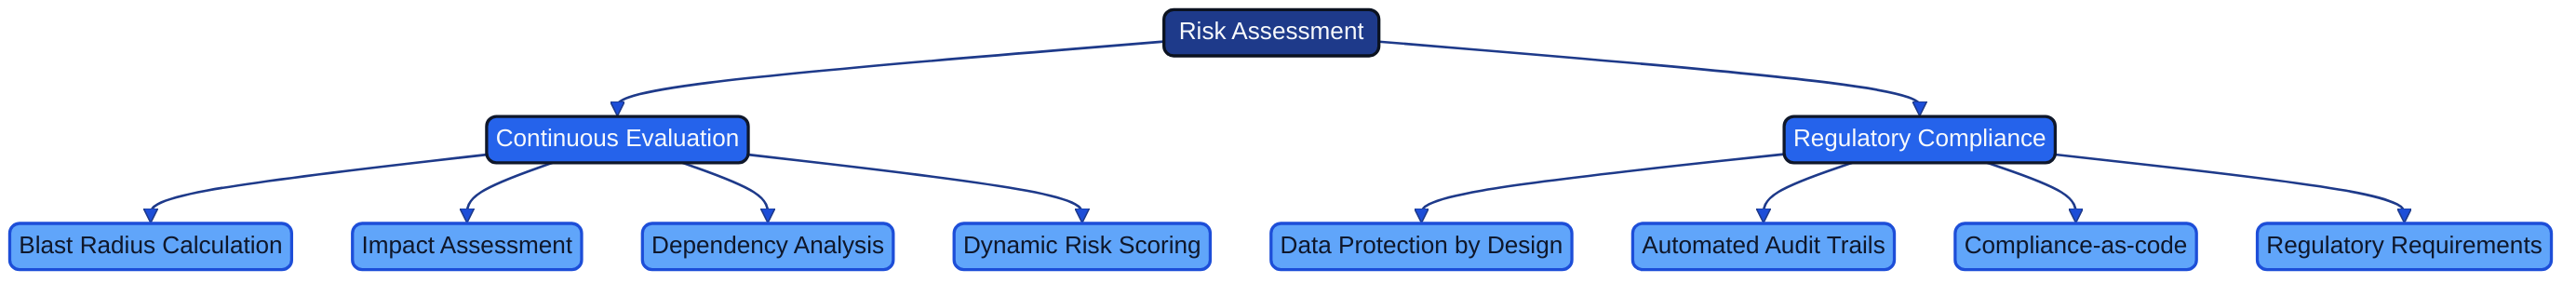
Architecture as Code programmes already encode infrastructure, policy, and security controls. Extending the repository to cover risk registers and threat playbooks makes the entire resilience posture transparent and repeatable.
Structure risk definitions as declarative YAML or JSON documents that capture context, probability, impact, and ownership, mirroring the likelihood-and-impact vocabulary of NIST SP 800-30 Source [83]. Version control provides historical records of changing assumptions and facilitates independent review. Treat the schema as a contract that automated tooling validates during pull requests.
statement: "Loss of regional database cluster availability disrupts customer journeys"
Primary topics explored
- Why risk and threat handling belong in the codebase
- Engineering a risk-as-code model
- Threat handling as code
- Integrating with the delivery pipeline
- Operating model considerations
- Sources
About Architecture as Code
Infrastructure as Code represents a fundamental change in how we manage and develop IT infrastructure. This book provides organisations with practical guidance for implementing IaC principles whilst fulfilling local compliance requirements and optimising costs.
The book covers everything from fundamental principles and tools to advanced implementation strategies, security aspects, and organisational changes required for successful IaC adoption.
IT architects, DevOps teams, developers, and decision-makers within organisations.

Gunnar Nordqvist
Conceived, directed and published the books of The Transformed Architecture.
Continue with the full chapter
Chapter 9C: Risk as Code and Threat Handling as Code in Architecture as Code gives the detailed explanations, practical examples and implementation patterns behind this summary.
This whitepaper belongs to “Security and Governance” and is one of 38 drawn from the manuscript.