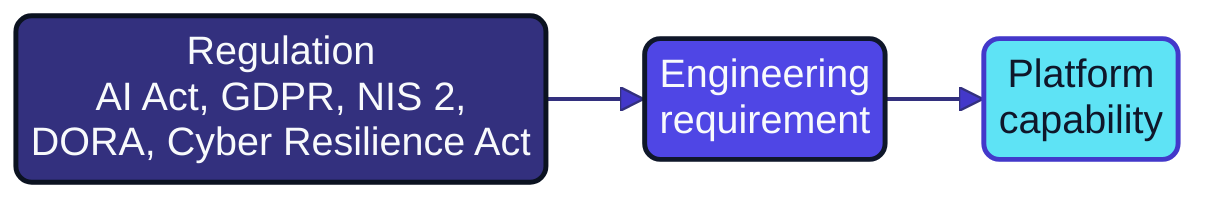
This chapter turns European regulation into the engineering requirements an AI platform has to meet, following each obligation from its instrument and article to the platform capability that satisfies it, the codified artefact that configures that capability, and the evidence the capability produces. It states each obligation only as far as the platform needs it; AI Governance, Chapter 3 gives the full legal treatment (73, Nordqvist, 2026). Everything here is architectural implication, not legal advice.
Platform engineers read regulation to establish structure. The requirement in Article 12 of the AI Act that high-risk systems "technically allow for the automatic recording of events" over their lifetime is, read as an engineer, a requirement for an append-only event store with a retention policy, a schema that identifies the system version, and an access path for the people who must read it (1, European Union, 2024).
If the platform offers each capability once, rather than forty projects building forty logging pipelines, a team meets the obligation by declaring that its system uses it, as Architecture as Code argued for infrastructure (72, Nordqvist, 2025). Every requirement below is therefore written as a chain:
Primary topics explored
- Reading regulation as an engineer
- Deciding which requirements apply
- High-risk requirements as platform capabilities
- Deployer and transparency obligations
- Post-market monitoring and serious incidents
- General-purpose AI models as supplier evidence
About AI Platform and Security
AI Platform and Security is Book 3 of The Transformed Architecture. It shows how large European enterprises and public authorities build, secure and operate the platform on which artificial intelligence runs: data, models and DevSecMLOps, retrieval and agents, infrastructure and sovereignty, AI security engineering, evaluation, observability and cost.
The companion volume AI Governance covers risk management, governance, assurance, organisation and leadership; Architecture as Code supplies the underlying discipline.
Platform engineers, security architects, MLOps teams, AI architects and technical decision-makers.

Gunnar Nordqvist
Conceived, directed and published the books of The Transformed Architecture.
Continue with the full chapter
Chapter 3: Regulatory Requirements as Engineering Constraints in AI Platform and Security gives the detailed explanations, practical examples and implementation patterns behind this summary.
This whitepaper belongs to “Foundations” and is one of 29 drawn from the manuscript.