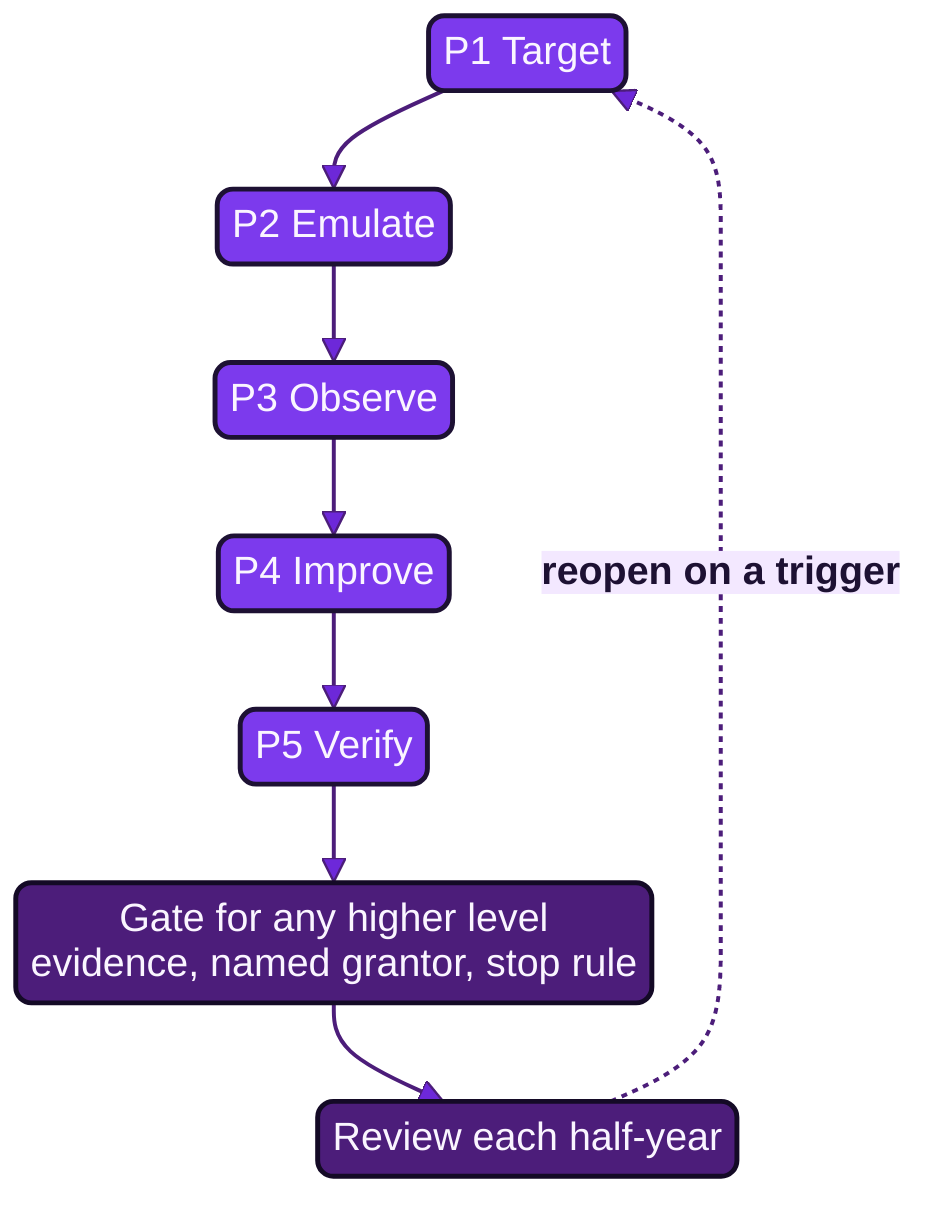
In January 2028 two governing bodies asked a question about the same practice. Nordvik Region's audit committee asked its chief information security officer (CISO) what the first threat-led exercise had proved, beyond a list of closed findings (AIDR-0800). Hansa Mutual's executive board asked its group CISO whether continuous automated red teaming made the quarterly purple session redundant (AIDR-0850). Chapter 27 followed four people through the twelve months to 2028-04-30, in which the loop answered. This chapter draws the year into a conclusion for each organisation and a comparison, and turns each conclusion into a plan for the next two years, recorded as AIDR-0849 for Nordvik and AIDR-0899 for Hansa. It concerns all five stages of the purple loop: P1 Target, P2 Emulate, P3 Observe, P4 Improve and P5 Verify.
Both organisations are fictional and the year is illustrative. The plans run from 2028-05-01 to 2030-04-30 and are adopted on 2028-04-29, the day before the first reports are due. The recommendations are the book's own conclusions from Chapters 4 to 26: they say what a good choice looks like given what the records showed, and they are not forecasts. The author's projections belong to Chapters 25 and 29. Wherever this chapter looks ahead it says whether the statement is observable, expected or speculation, in the sense of AI Governance, Chapter 22 (88, Nordqvist, 2026).
The series makes one argument: keep decisions as records that can be corrected, keep the ability to stop outside the system being stopped, keep people able to do the work and judge the output, keep dependence reversible and match autonomy to reversibility (91, Nordqvist, 2026). AI Blue applied it to the team that defends and added a closing rule for the loop: a finding is closed only when its re-test passes (94, Nordqvist, 2026). AI Red Team supplied the five record states and the autonomy levels on which the delegation profiles of this book rest (90, Nordqvist, 2026). European law adds that accountability stays with named people: NIS 2 Article 20 places the approval and oversight of cybersecurity risk-management measures on the management body, and DORA Article 5 does the same for the management body of a financial entity (3, European Union, 2022) (2, European Union, 2022). The Transformed Security Architect drew the architectural consequence, that someone must turn each article into a control and that accountability cannot be delegated to a system (92, Nordqvist, 2026).
Primary topics explored
- What the year established
- Nordvik Region: a bought loop
- Hansa Mutual: a run loop
- A comparison
- The five-part thesis, as each organisation answers it
- The next two years
About AI Purple
AI Purple is Book 9 of The Transformed Architecture. It takes the loop between the red team and the blue team as its subject and asks what happens when AI sits on both sides of the table: the five stages of the loop (target, emulate, observe, improve, verify), rules of engagement and safe emulation, continuous emulation, the independence principle, coverage as a claim that needs evidence, the loop's own AI and how to defend it, operating models, decision rights, regulation, and the people involved, for European enterprises and public authorities.
It builds on the conclusions of Architecture as Code, AI Governance, AI Platform and Security, AI Red Team, AI Threat, The Transformed Security Architect, AI Boss and AI Blue.
Chief information security officers, heads of security operations, red-team leads, penetration testers, SOC managers, detection engineers, purple-team coordinators and incident commanders, security and AI architects, boards and management bodies, procurement leads, works councils and unions, data protection and audit functions, and public-sector leaders.

Gunnar Nordqvist
Conceived, directed and published the books of The Transformed Architecture.
Continue with the full chapter
Chapter 28: Nordvik Region and Hansa Mutual: Conclusions for Two Organisations in AI Purple gives the detailed explanations, practical examples and implementation patterns behind this summary.
This whitepaper belongs to “Experience and Conclusions” and is one of 33 drawn from the manuscript.